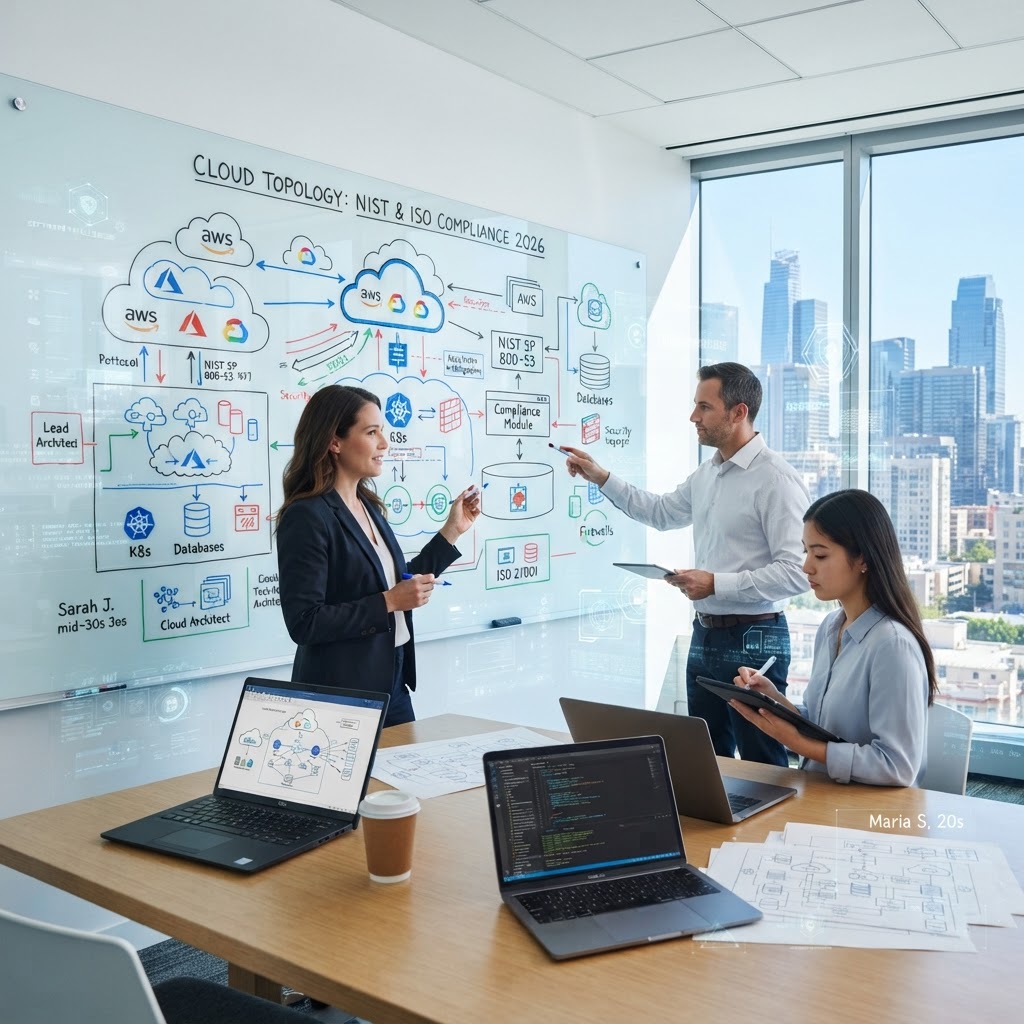
As we approach 2026, the cloud compliance landscape has shifted from a "check-the-box" regulatory exercise to a core component of enterprise risk management. For B2B organizations, the convergence of evolving NIST frameworks and updated ISO standards represents both a significant operational hurdle and a powerful competitive advantage. At SoftwareVerdict, our research consistently indicates that companies with robust, automated compliance postures see a 30% reduction in sales cycle friction when dealing with security-conscious enterprise procurement teams. However, as organizations transition to complex multi-cloud and hybrid architectures, achieving alignment with these standards requires more than policy documentation; it demands a fundamental shift toward continuous compliance monitoring and automated governance.
The Evolution of NIST 800-53 and the 2026 Reality
The National Institute of Standards and Technology (NIST) remains the gold standard for federal and high-security commercial environments. As of early 2026, the adoption of NIST 800-53 Revision 5 (and its subsequent updates) has become the de facto baseline for organizations managing critical infrastructure and sensitive data. The primary evolution we have observed in the field is the shift from perimeter-based security controls to a data-centric, Zero Trust architecture.
Key Focus Areas for 2026:
- Supply Chain Risk Management (SCRM): NIST now places a heavier emphasis on third-party risk. Organizations must demonstrate visibility into their SaaS dependencies.
- Continuous Monitoring: Static, point-in-time audits are no longer sufficient. NIST 800-53 integration now mandates real-time telemetry from cloud control planes.
- Zero Trust Architecture (ZTA): NIST SP 800-207 guidance is being baked into every control, moving away from simple network segmentation toward identity-based micro-segmentation.
In our experience at SoftwareVerdict, the most common pitfall for enterprises is attempting to map legacy on-premises controls directly to cloud services. Cloud Service Providers (CSPs) like AWS, Azure, and Google Cloud offer "Shared Responsibility Models," but the granular configuration—specifically regarding identity and access management (IAM) and encryption at rest—remains the client's burden. Misconfiguration, according to recent research from Gartner, remains the primary cause of cloud security incidents, accounting for over 95% of breaches.
ISO/IEC 27001:2022 and the Rise of Integrated Management Systems
While NIST provides the technical "how-to," ISO/IEC 27001 remains the global language of security management. The 2022 update, which has reached full maturity in the 2026 market, introduced essential changes to Annex A controls, specifically addressing threat intelligence, cloud services, and physical security in remote work environments.
"The integration of ISO 27001 into the operational DNA of a software company is no longer an IT project; it is a board-level imperative. Organizations that fail to demonstrate ISO-level maturity face a narrowing pool of enterprise customers who prioritize supply chain integrity above all else." — SoftwareVerdict Lead Analyst Team
Nuances in ISO Implementation:
Expert practitioners recognize that the true value of ISO 27001 lies in its risk-based approach. Unlike rigid checklists, ISO demands that the organization define its own risk appetite. For a B2B SaaS platform, this means your Statement of Applicability (SoA) must clearly articulate how you handle multi-tenancy isolation—a technical nuance that is often overlooked in smaller startups but scrutinized heavily by enterprise buyers.
Managing Trade-offs: The Compliance-Agility Dilemma
Achieving total compliance with both NIST and ISO standards creates an inherent tension between security posture and development velocity. Implementing stringent controls—such as mandatory multi-factor authentication (MFA) for every API call or complex, rotating encryption key management—can introduce latency into CI/CD pipelines. This is the "compliance-agility dilemma."
To mitigate this, industry leaders are adopting "Compliance-as-Code" (CaC) methodologies. By embedding compliance checks into the development lifecycle, security teams can prevent non-compliant infrastructure from ever being deployed. However, we must be transparent about the limitations: CaC is not a silver bullet. It requires significant engineering overhead to build and maintain, and it cannot replace the human intuition required for threat modeling and sophisticated architectural review. For many mid-market firms, the trade-off is either investing in an internal DevSecOps team or outsourcing to specialized compliance automation platforms.
Strategic Alignment: Mapping NIST to ISO
One of the most frequently asked questions we receive at SoftwareVerdict is: "Can we use one framework to satisfy the other?" While NIST 800-53 and ISO 27001 differ in structure—NIST is prescriptive and technical, while ISO is management-focused and risk-based—they are highly synergistic. Mapping these frameworks allows organizations to streamline their evidence collection process.
Best Practices for Framework Harmonization:
- Control Mapping: Use a unified control framework (UCF) to map common requirements. For example, a single process for incident response can satisfy both NIST IR controls and ISO A.16 controls.
- Unified Evidence Store: Create a centralized, immutable log of security events. This serves as the single source of truth for both internal security metrics and external audits.
- Cross-Functional Audits: Move away from departmental siloed audits. Conduct unified audit cycles that assess both technical controls (NIST) and management policy adherence (ISO) simultaneously.
By harmonizing, organizations can reduce the burden of audit preparation by approximately 40%. However, do not assume that a clean ISO audit guarantees full NIST compliance; the latter requires deeper technical scrutiny of system-level configurations that ISO simply does not reach.
The Future of Cloud Compliance: AI-Driven Governance
Looking toward the next 18 months, we expect AI-driven compliance automation to become the market standard. Tools that ingest cloud logs to detect compliance drift in real-time are moving from "nice-to-have" to "essential." As organizations move toward 2026, the reliance on automated governance platforms will grow, as the sheer volume of cloud-native services makes manual oversight impossible.
However, an expert warning is necessary here: AI-driven governance tools require high-quality data input. If the underlying security architecture is flawed, the AI will simply report on that flaw more efficiently. As noted by the Cloud Security Alliance (CSA), the "garbage in, garbage out" principle is amplified in automated compliance systems. Therefore, human-in-the-loop validation remains a non-negotiable step in any robust compliance program.
Conclusion and Recommendations
Navigating the compliance environment of 2026 requires moving beyond the mindset of static documentation. The convergence of NIST and ISO frameworks into a continuous, automated workflow is the only viable path for B2B organizations seeking to scale in a security-conscious market. While the technical investment is substantial, the ROI—manifested in shortened sales cycles, reduced risk of breach-related litigation, and enhanced brand equity—is clear.
For organizations currently benchmarking their compliance posture, we recommend a three-step approach: audit your current infrastructure against the NIST 800-53 Rev 5 control set, harmonize those requirements with your ISO 27001:2022 management system, and integrate automated monitoring tools to capture evidence continuously. At SoftwareVerdict, we help organizations identify the right tooling and architectural strategies to meet these demands without stalling innovation.
Ready to benchmark your compliance maturity? Explore our 2026 Security Procurement Reports to see how your stack compares to industry standards and gain actionable insights into optimizing your cloud governance.
Transparency Note: SoftwareVerdict provides objective analysis and research. Our insights are derived from independent data, client interviews, and technical benchmarking. We do not receive commissions from the vendors mentioned in our research, and our assessments remain neutral regardless of commercial partnerships.